TIER-4 is a pre-tuned, AI-agentic security operations solution — a product and a service layer that deploys as a Splunk app, alongside or inside your existing SOC, and delivers real detection from day one.
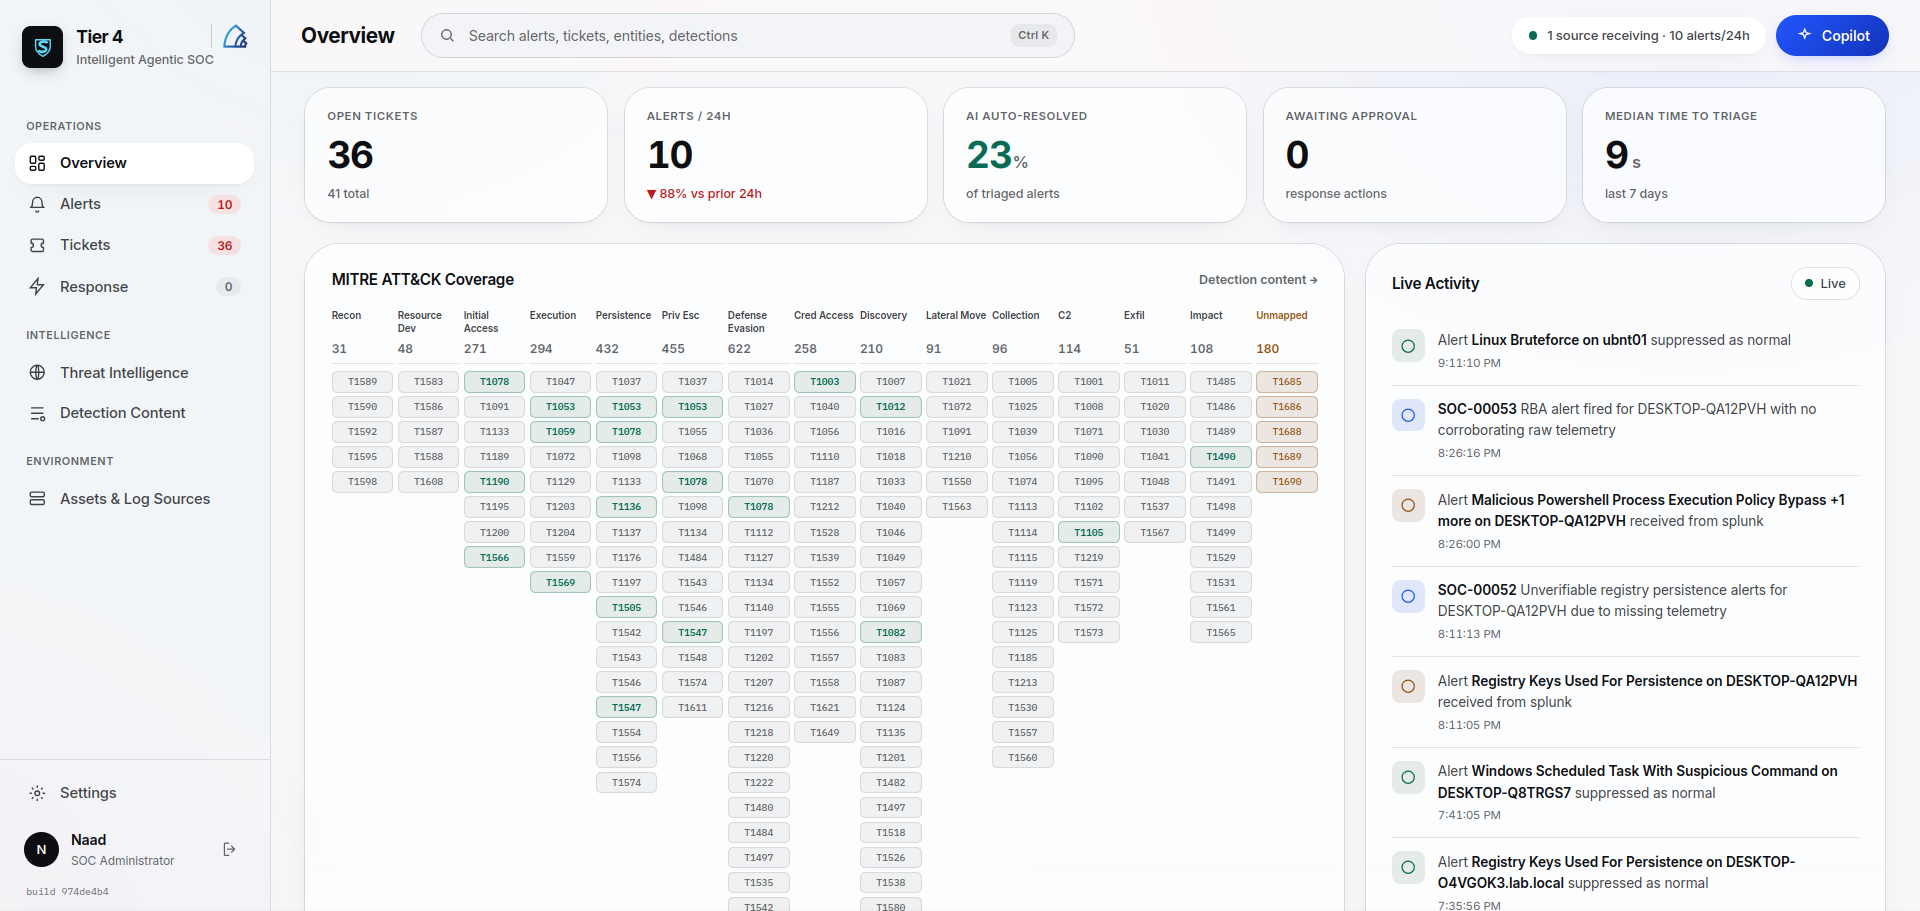
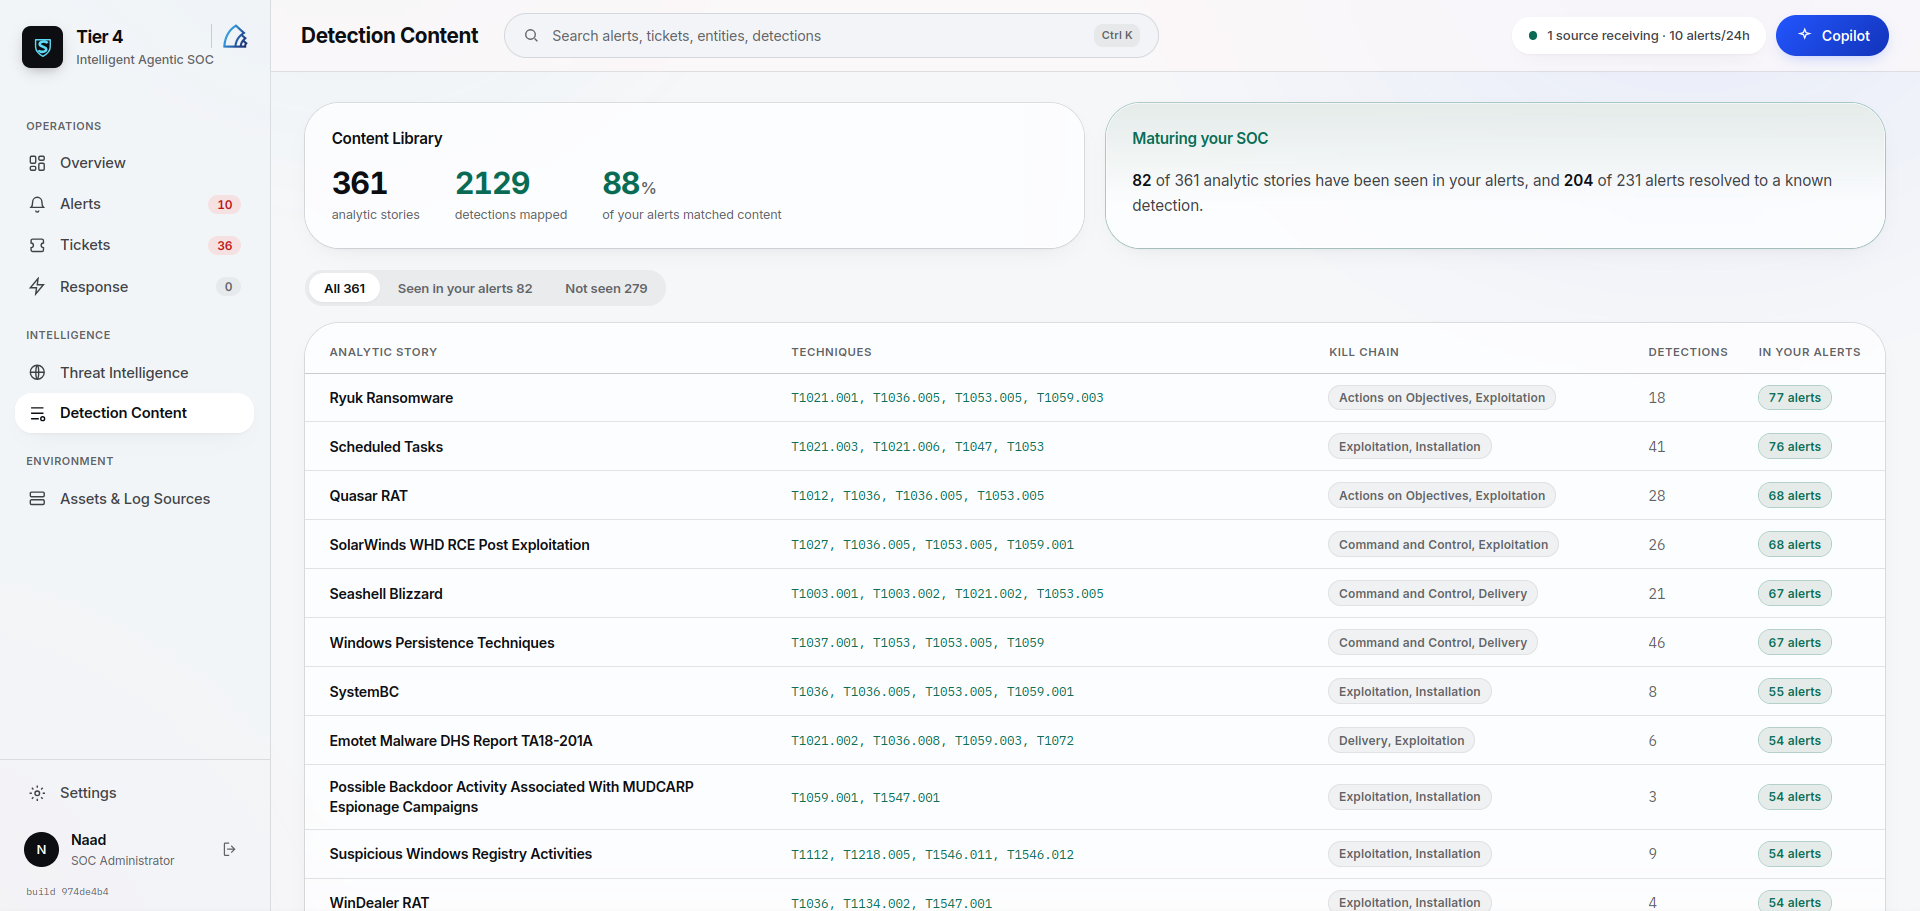
TIER-4 ships with a battle-tested detection library, so you get coverage the moment telemetry starts flowing — not at the end of a multi-month build.
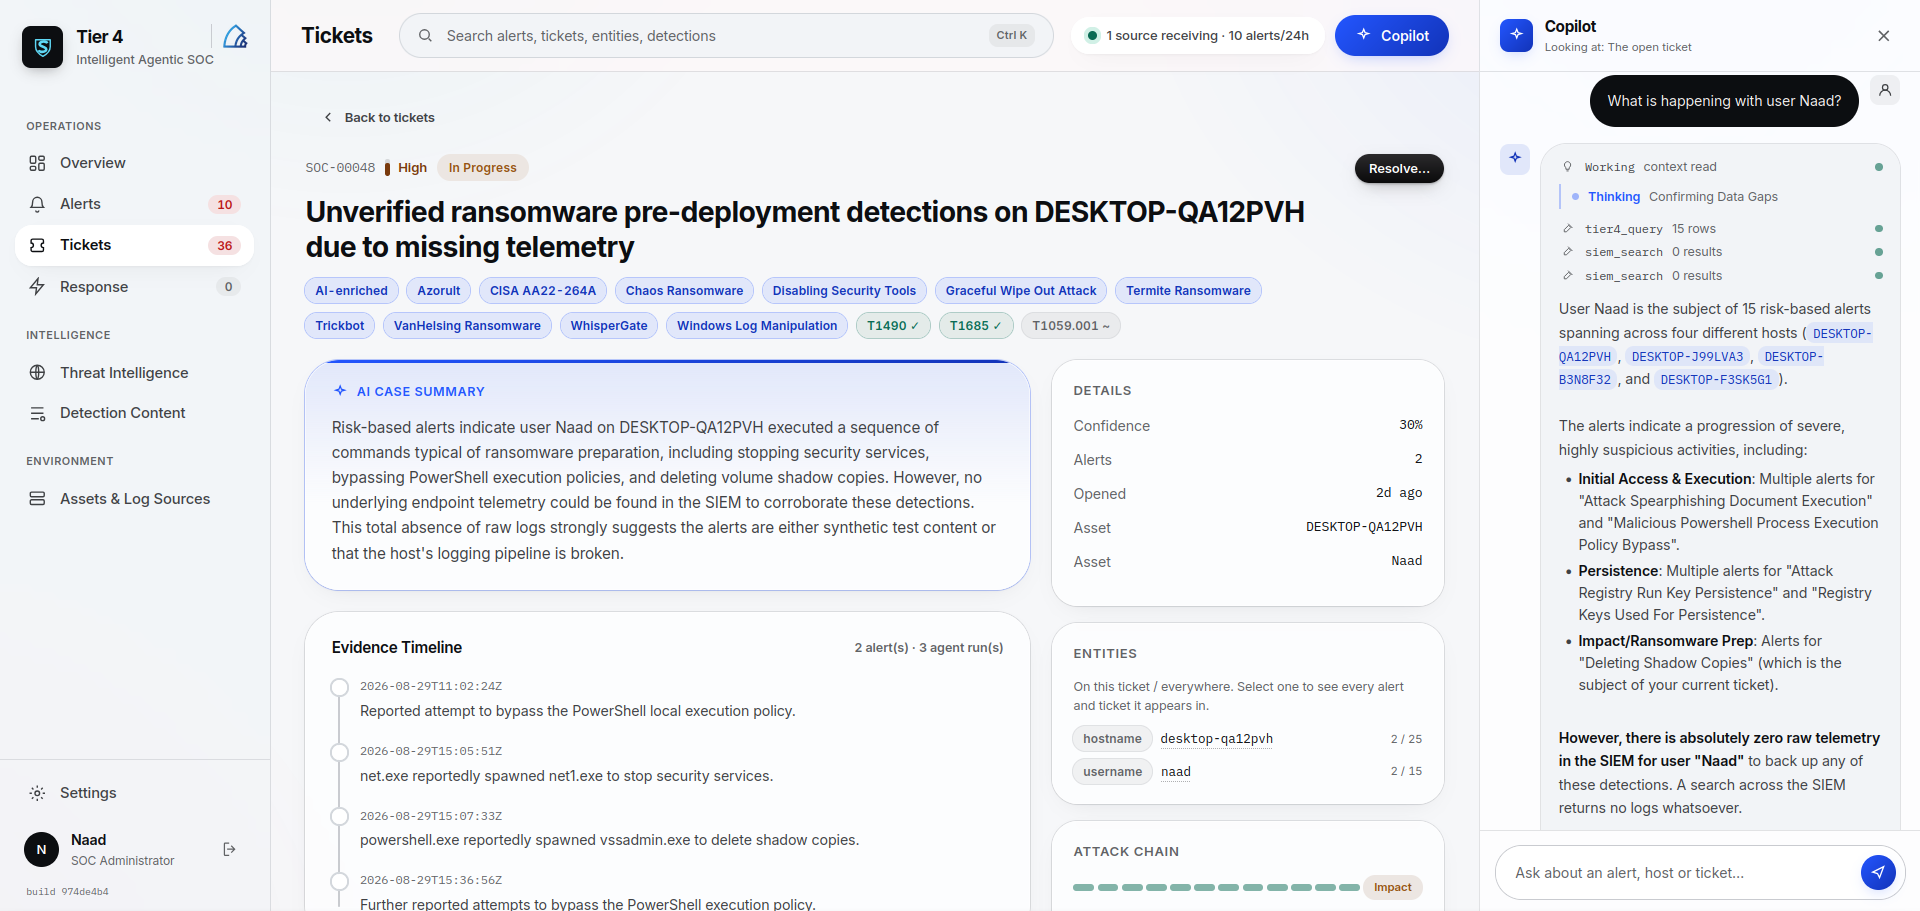
AI agents triage and enrich alerts, promote the ones that matter into tickets, and explain every decision. Tier 2 opens a case that is already assembled.
Based on our experience, logs from any environment — including Kubernetes — are onboarded with the lowest possible overhead, then tuned so detection actually works on your data.
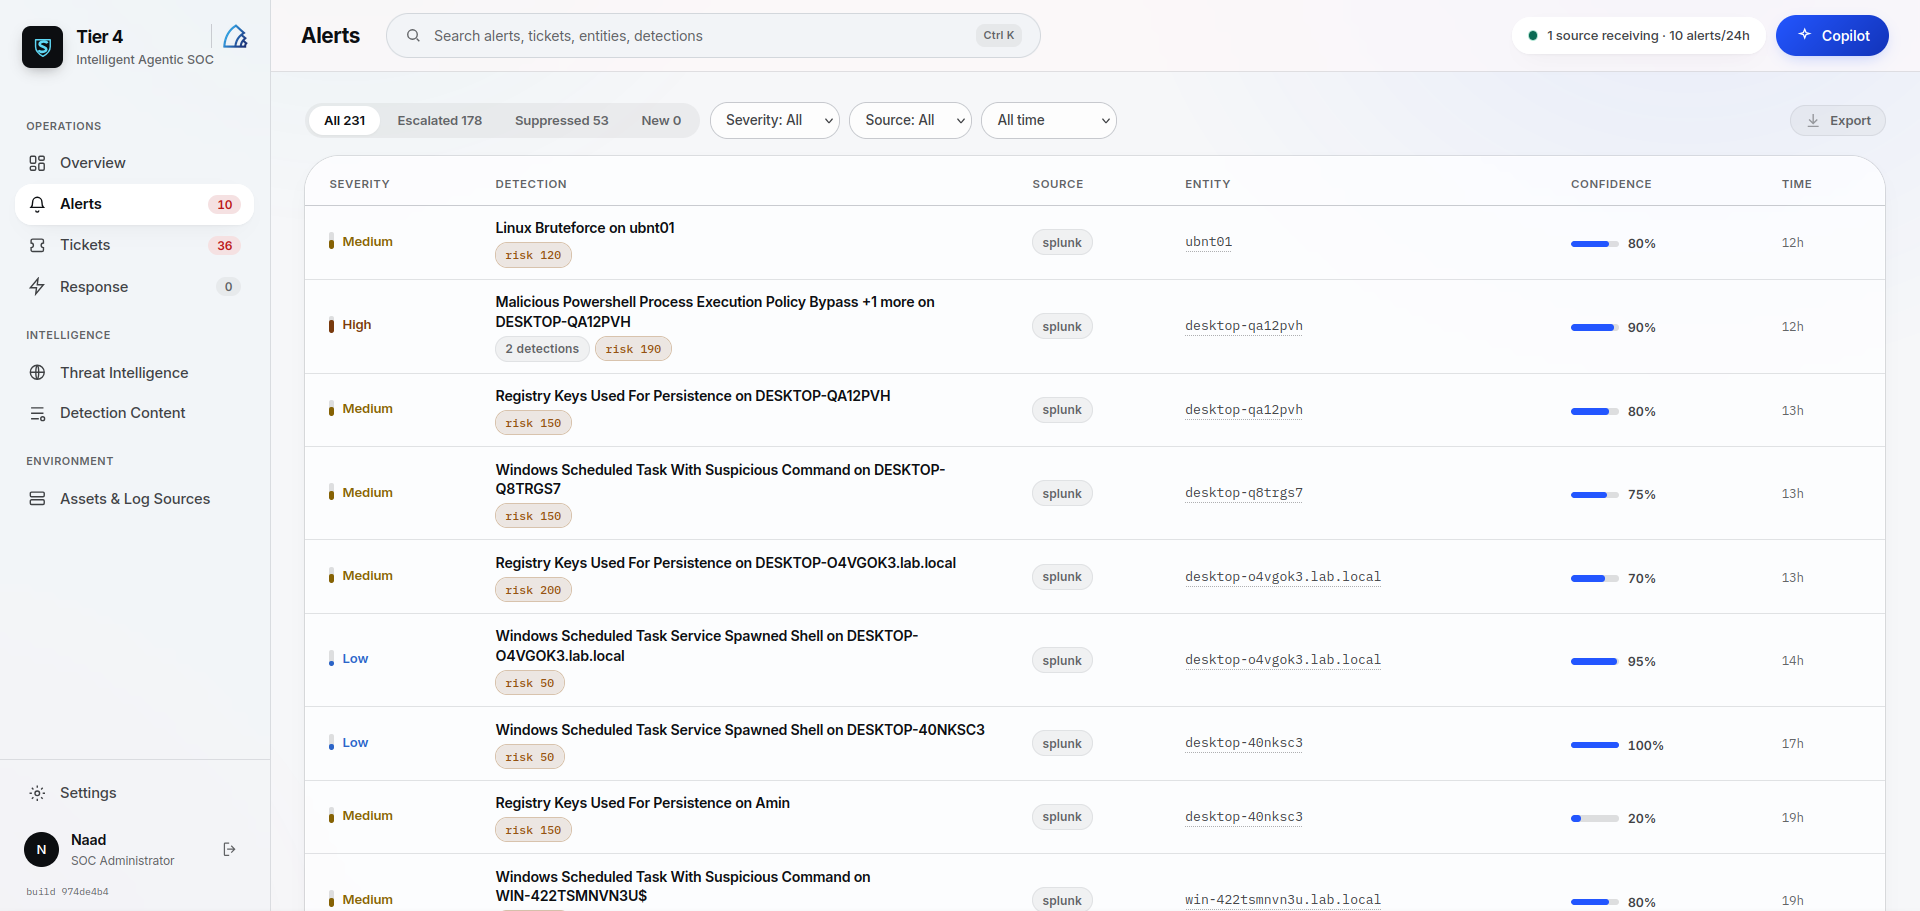
A product plus a service layer that together cover the whole organization — from infrastructure to forensics.
The attack scenarios that matter, ready from the first day of deployment.
Minimal false positives, so analysts spend time on real threats.
Every rule validated with attack & breach simulation tooling.
Tuned alerts feed the AI — not raw or untuned logs — cutting token cost dramatically.
No rip-and-replace. Your SOC keeps its tools, processes, and ownership.
When your current SOC is Splunk-based and compatible, TIER-4 integrates directly onto the same platform — one unified environment.
TIER-4 is deployed next to your existing SOC. Forward a copy of your logs and get a second, already-tuned detection capability — fast.
From infrastructure hardening to forensics, every layer is in one integrated package.
Pre-tuned content means real visibility and detection during onboarding — not months later.
Automation removes the Tier 1 bottleneck while staying under analyst approval and control.
Every engagement leaves capability behind, pulling your own SOC toward a higher standard.
Integrates onto a compatible SOC, or deploys alongside — without disrupting your tools.
Built by a team with over a decade in IT security — depth shown in Tier 3 and forensics.
Book a demo and we'll show working detection, AI triage, and supervised response — running as a Splunk app next to your SOC.
For products, security services, a TIER-4 demo or PT reselling, fill in the form and our team will get back to you.